Critical vulnerability in Oracle E-Business Suite. Patch is necessary

Marije Politiek • 2 juli 2020

MCX recommends that the same patch implement the SameSite Cookie in the Oracle E-Business Suite. This makes your environment less prone to cross-site request forgery (CSRF).


There is a patch for both EBS 12.1 and 12.2 available.

More information can be found at:

https://blogs.oracle.com/ebstech/samesite-cookie-attribute-now-available-for-ebs-122-and-ebs-1213

Recent news

Why MCX has been in existence for over 25 years
door Marije Politiek • 8 oktober 2026
and why that is now more important than ever for the Public Cloud
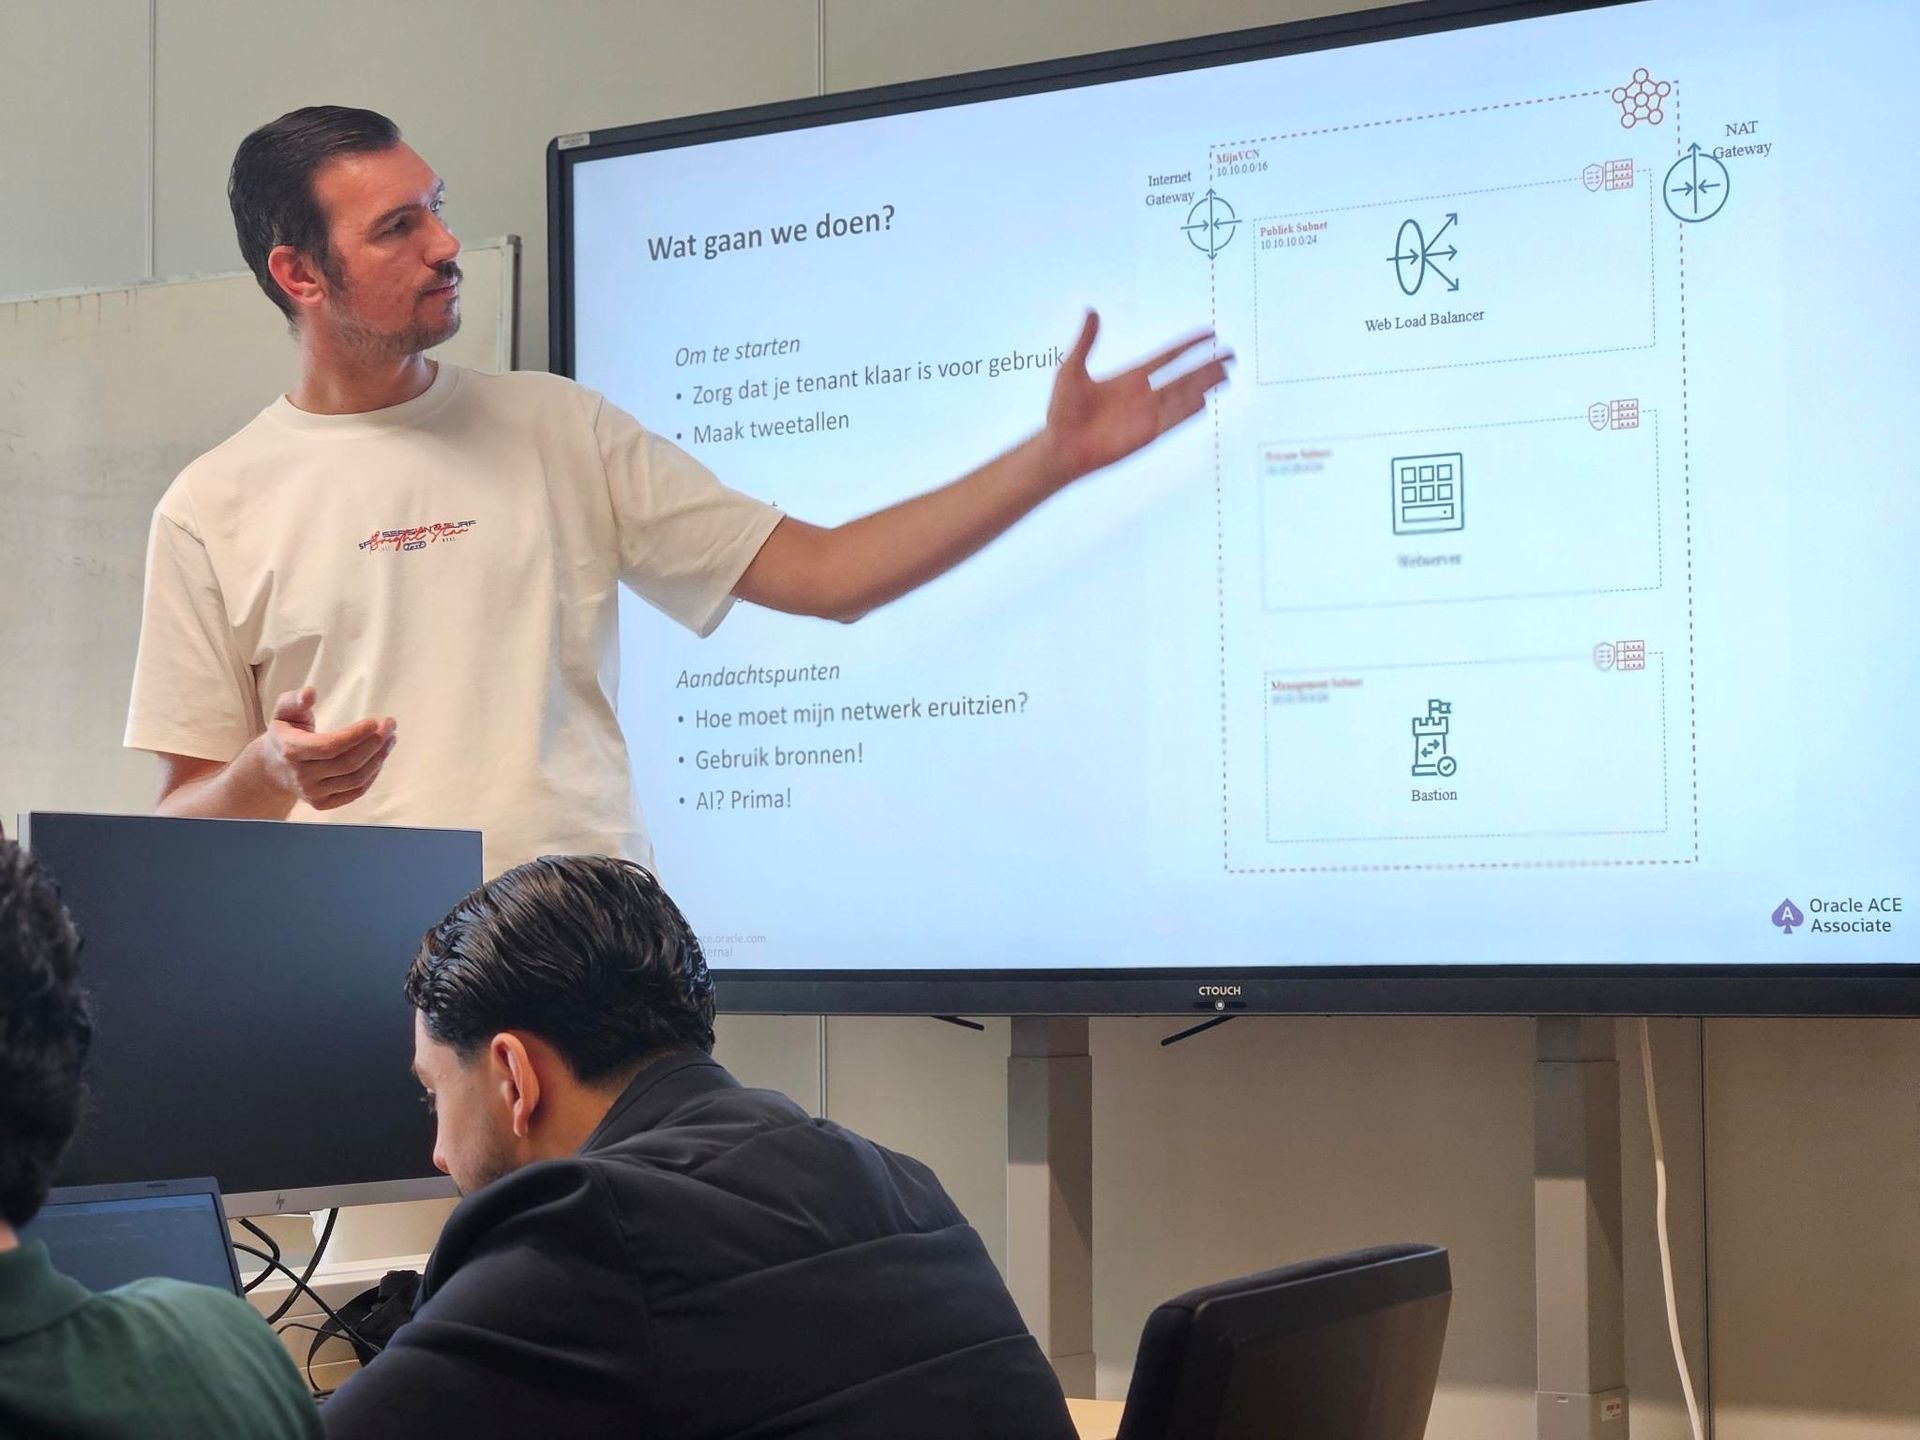
a real deep dive into the practicalities of working as an IT Service Provider
door Marije Politiek • 27 mei 2026
From the classroom to cloud-based practice
MCX log4shell
door Marije Politiek • 4 december 2025
MCX updates customers on the Log4Shell vulnerability affecting Oracle products. Patches are pending; mitigation steps and monitoring are already in place.