Spring4Shell

Marije Politiek • 1 april 2022

As of yesterday, March 31st 2022, the Dutch NCSC warns organizations for a vulnerability in the Spring Core Framework. This vulnerability has been designated as CVE-2022-22965 and is referred to with the more readable name Spring4Shell. This vulnerability allows a remote and unauthenticated attacker to execute random code. The corresponding CVSS score of the vulnerability is 9.8. This is a very critical vulnerability which is similar to the Log4Shell vulnerability of last December in terms of impact.

To exploit this vulnerability a few requirements must be met:


  • the service must use JDK version 9 or higher.
  • the service must be based on Tomcat.
  • the servlet, executed by the Tomcat service, must not be executed as a jar but as a war file.
  • the service must use Spring Framework versions 5.3.0 to 5.3.17, 5.2.0 to 5.2.19 and older versions.
  • the service must use files who's name start with spring-beans-.


MCX is currently investigating which customers are affected. If a customer is indeed affected, MCX will initiate communication via the regular channels.

If you have additional question, please contact MCX at +31 55 5260670 and ask for the Security Officer.

Recent news

Why MCX has been in existence for over 25 years
door Marije Politiek • 8 oktober 2026
and why that is now more important than ever for the Public Cloud
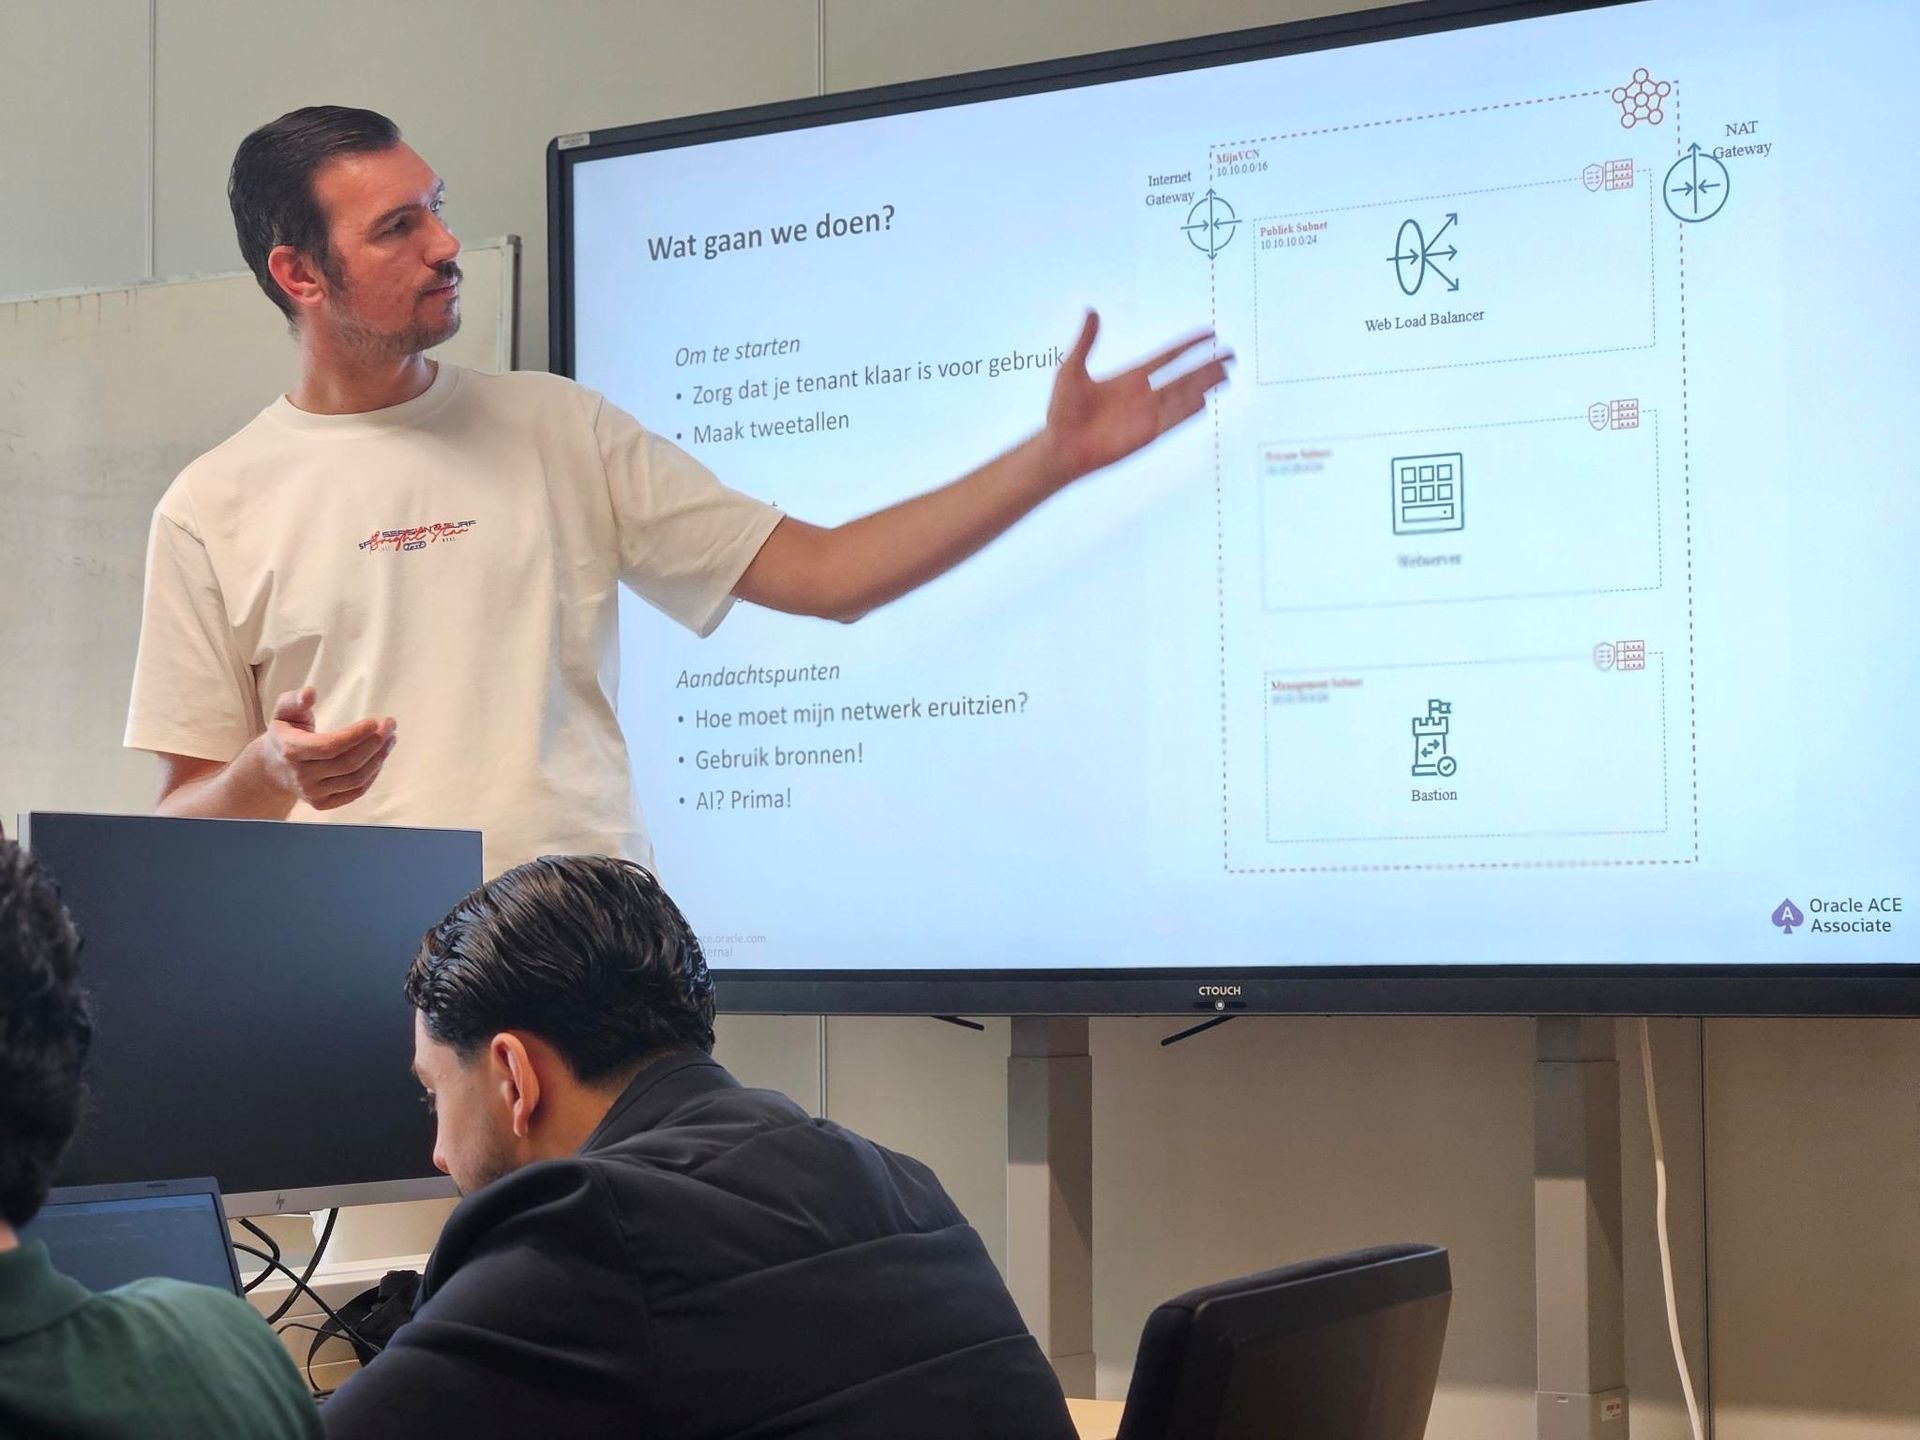
a real deep dive into the practicalities of working as an IT Service Provider
door Marije Politiek • 27 mei 2026
From the classroom to cloud-based practice
MCX log4shell
door Marije Politiek • 4 december 2025
MCX updates customers on the Log4Shell vulnerability affecting Oracle products. Patches are pending; mitigation steps and monitoring are already in place.